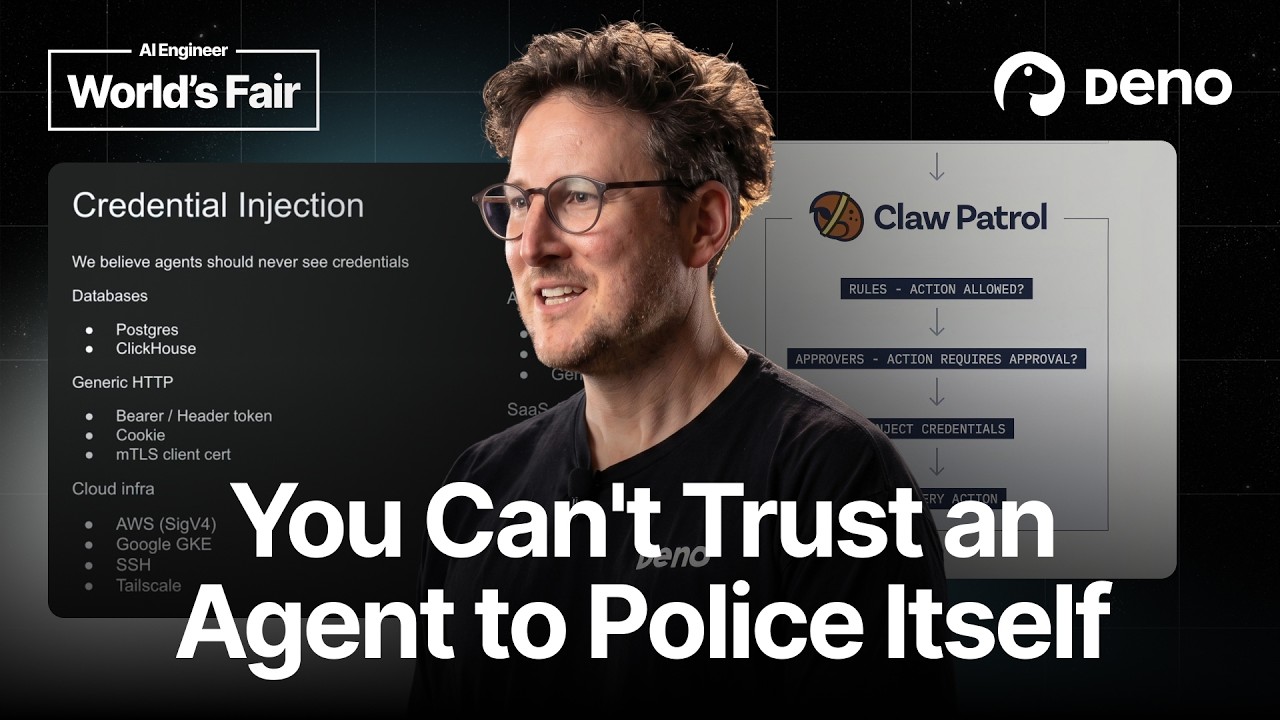
Imagine an AI agent that can fix production incidents on its own — until a sneaky prompt tries to make it delete your user database.
The Simple Version
Think of an agent as a helpful robot that can open any door in your house. If the robot is tricked, it might open the wrong door and cause chaos.
How It Actually Works
Guarding at the Byte Level
Claw Patrol sits in front of the agent and reads every outgoing byte, even when the traffic isn’t HTTP.
Hard‑to‑Spot tunnels
Even if the agent uses psql or SSH, the proxy sees the raw protocol and can block it.
Rule language in HCL
These recipes are written in HashiCorp Configuration Language (HCL), unit‑tested, and stored in Git.
Technical Deep Dive
The proxy runs as a Deno process that loads rule files of roughly a thousand lines.
Each rule matches on protocol identifiers, ports, and payload patterns to decide whether to allow or reject.
Credentials such as database passwords or OAuth tokens are injected into the proxy, never exposed to the agent.
When a rule matches a dangerous action, the proxy can route the request to an LLM judge, post it in Slack for human review, or automatically deny it.
Protocol plugins let the proxy understand low‑level streams like PostgreSQL’s wire protocol, ensuring that a “DROP TABLE users” command is caught before it reaches the database.
Why This Matters
Agents that control production systems are powerful but inherently untrusted.
Without a byte‑level guard, a single prompt injection can bypass all higher‑level safeguards.
Claw Patrol provides a deterministic, testable barrier that works regardless of how the agent tries to communicate.
This approach shifts security from hoping the model stays obedient to enforcing hard limits at the network edge.
Key Takeaways
- Agents with broad access need a low‑level, byte‑level guard.
- Claw Patrol inspects every outgoing byte, even non‑HTTP traffic.
- Rules are written in HCL, version‑controlled, and unit‑tested.
- Credentials are held by the proxy, keeping them hidden from agents.
- The system can route suspicious actions to LLM or human reviewers.
- Protocol plugins enable detection of database‑level commands.
- Security becomes a deterministic gate, not wishful thinking.