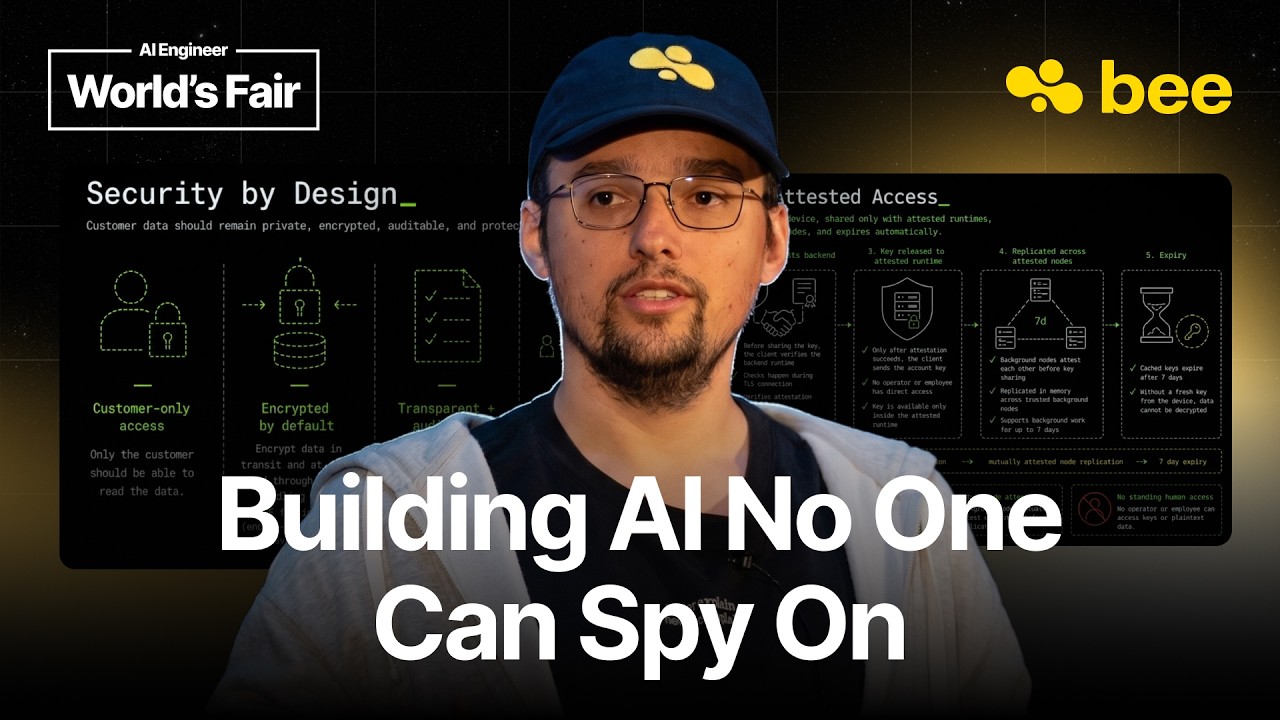
Imagine a tiny device that records everything you say and learns your secrets faster than you think.
The Simple Version
Bee’s mission is simple: lock your data so only you can ever see it.
How It Actually Works
Attestation & Transparency Log
The phone checks the exact code before sending data.
Confidential Compute & Expiring Keys
Models run in a protected enclave and memory keys vanish after seven days.
Signing & Insider Protection
A separate privacy team holds signing keys that Bee can’t change.
Technical Deep Dive
Bee’s core is about 20,000 lines of memory‑safe code, most of which just verifies attestation.
No custom crypto is used; everything relies on existing secure primitives.
Inference runs on Bee’s own models inside AWS Nitro enclaves, keeping keys only in RAM.
Why This Matters
When a device can capture a year’s worth of conversation, trust must be built on math, not on policy.
Enterprises and users alike need guarantees that even the platform owner cannot peek.
This model shows a path to AI agents that act continuously without sacrificing privacy.
Key Takeaways
- Keys never leave your phone and are destroyed after a week.
- Attestation uses a public log (Sigstore) for anyone to verify code.
- Confidential compute isolates inference from the rest of the cloud.
- Signing keys are stored by a separate privacy team to prevent covert changes.
- The system is tiny (20,000 lines) and avoids homegrown crypto.
- It proves privacy can coexist with powerful on‑device AI.
- Trust is shifted from the cloud provider to verifiable mathematics.