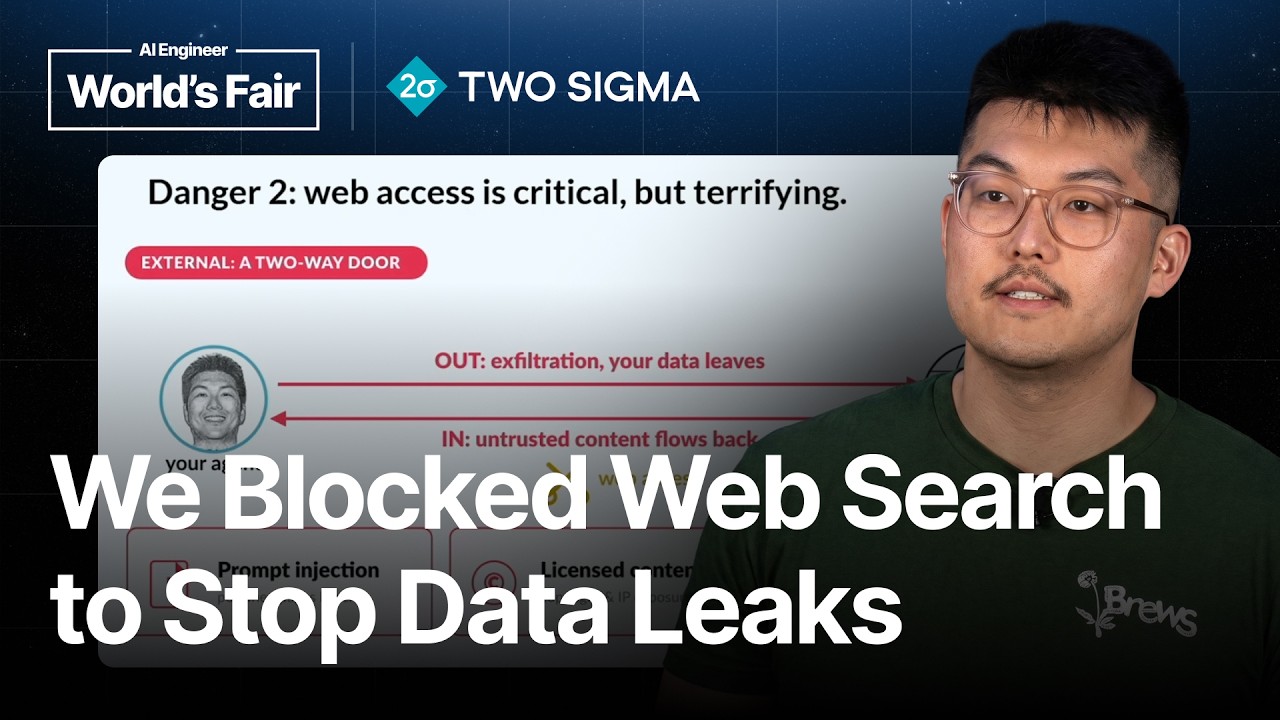
Imagine every quant at a hedge fund having a digital twin that acts exactly like them in the cloud.
The Simple Version
The idea is simple: instead of a generic service account, each person gets a personal cloud “agent” that uses their real identity.
Think of it like a clone in a horror movie that can slip away and cause trouble if not tightly controlled.
How It Actually Works
Agent Identity
Running the agent as the user erases traditional permission boundaries.
Namespace Infrastructure
Two Sigma already had a Kubernetes namespace per person in each region, built for automated jobs.
Trace Header
They propagate a header like a trace ID, linking every result back to the human who started it.
Technical Deep Dive
Each region runs its own namespace, isolated from others, so workloads never share a pod with a different employee.
The sidecar container receives the user’s identity token and injects it into the pod environment, making the process think it is the real user.
Permissions are tied to the individual’s corporate credentials, so licensing checks happen at the OS level, not at the service level.
When a model needs the open web, they block direct internet calls and instead use a private search index that lives inside the network boundary.
This “web grounding” gives them 24‑hour freshness while keeping crawlers and bots confined, reducing exposure to prompt injection and data leakage.
Why This Matters
For regulated firms, the ability to run code as a real person simplifies compliance but creates a new attack surface.
If an agent is compromised, attackers can masquerade as any employee, making detection harder.
By limiting web access and using internal search grounding, they trade freshness for security, a calculated risk that hedging funds can afford.
Key Takeaways
- Personal agents replace generic service accounts.
- Kubernetes namespaces give per‑user isolation.
- Trace headers expose the full execution chain.
- Web grounding blocks direct internet, limiting freshness.
- Security gains outweigh the freshness cost for regulated firms.